Cloud Threat Gamification: Lessons Learned and How to Set One Up
summary
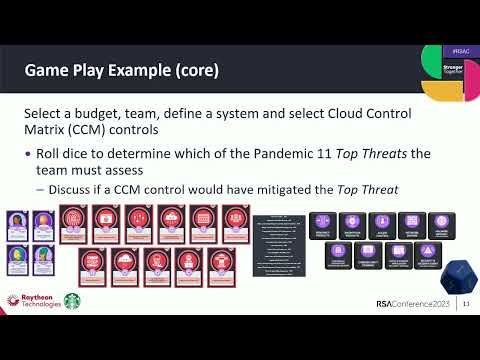
A playable tabletop that turns CSA’s pandemic 11 into a budgeted threat model uses dice (or cards), role cards and a $5M budget to buy mitigations across SaaS/PaaS/IaaS and staff; organizers run 40 minutes setup plus ~80 minutes gameplay and have run it five+ times. Lessons: randomness from dice vs cards skews outcomes, attendees need ready sample systems, scorecards beat custom cards, groups game hiring rules, and the advanced version is fun but requires rehearsal to work.
AI-written summary · about
chapters (13)
- 0:00Introduction and speakers
- 3:19Game concept and title
- 4:52Pandemic 11 and threat modeling
- 7:45Game mechanics and budget
- 10:42Top threats survey and deep dives
- 15:30Lessons learned from testing
- 21:16Training objectives and challenges
- 26:40Game variants and card systems
- 31:22Incident response and randomness
- 34:12Gaming the system and team roles
- 37:34Example systems and controls
- 44:11Conclusion and next steps
- 45:42Q&A session
related talks
 31m📙 Level Up Your Threat Modeling: Turning Security Into a Team Adventure 🖥️
 34mHack Your Board's Mindset: Closing the Strategy-Operations Gap via Board Game Simulations
 39mChaos Stack: Designing Layered Tabletop Exercises for Complex Crisis Simulation
 01h 08mBackdoors & Breaches: Live Tabletop Exercise Demo
 59mBackdoors & Breaches: Live Tabletop Exercise Demo
 30mShall We Play a Game?
 27mArcades and Audits: What Gaming Can Do for Your Security Posture
 20mPlay, Learn, Secure: The Power of Gamification in Security Training