Security Challenges of Cloud Native Companies with Remote Workers
summary
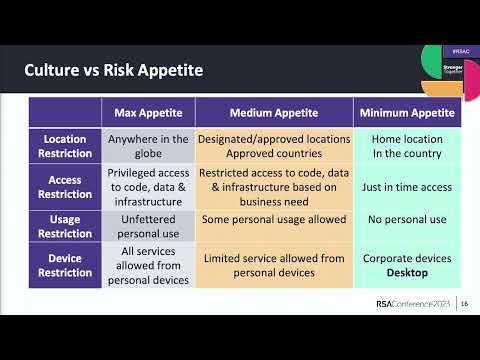
Argues that remote work raises concrete risks and prescribes concrete controls: classify connections as Max/Partial/Minimal/No Trust and enforce device trust boundaries with agents that detect network and Wi‑Fi, feed a central trust calculation, and adapt MFA, timeouts and credential caches. Replace permanent privileges with just-in-time access revoked by cron or IaC, require cloud IDEs and infrastructure as code, enforce field‑level encryption, vet high‑risk vendors (Maersk‑style supply‑chain example), and practice incident playbooks frequently.
AI-written summary · about
chapters (9)
- 0:00Start
- 0:42Corporate Risk Appetite Is Evolving
- 7:15Risk of Public Workspace
- 9:12Mitigate Location Risk
- 10:49Device Usage Experience Changes with Trust Level
- 12:10Device Access Changes with Trust Level
- 14:23Calculate Trust Level
- 16:53Access Risk Appetite
- 25:13Other Risk of Remote Workforce
related talks
 30mSecurity Awareness with a Remote Team
 48mControlling Clouds: Beyond Safety
 25mSecurity, Identity - Back to the Drawing Board?
 40mTen Things to Include in Remote Work IT Risk Assessments
 23mCloud Native Security for the Rest of Us
 41mPanel: Securing Cloud Native Applications
 35mCloud Native Security for the Rest of Us
 41mCloud Native Security For The Rest Of Us