Bon Appetit: Establishing an Effective Cyber Risk Appetite
summary
Argues that practical cyber risk appetite needs explicit thresholds, KPIs/KRIs/KCIs and consistent risk analysis rather than vague statements, and points to guidance such as NIST IR 8286 and 12 CFR Part 30 and industry methods like OCTAVE FORTE and FAIR. Recommends three metric sets—risk exposure, control performance including testing, and shock resilience—reports quarterly, classifies scenarios as within / approaching / exceeding appetite, and shows concrete examples (a 4,002‑record loss and outages of 4, 6, 14 hours) to map incidents to thresholds.
AI-written summary · about
chapters (19)
- 0:00Intro
- 1:02Disclaimer
- 2:56What is a risk appetite?
- 7:07Cyber risk appetite statement fundamentals
- 9:03Risk appetite statement effectiveness issues
- 12:27Explicit and succinct scenario statement example
- 16:12Cyber risk tolerance adherence actions
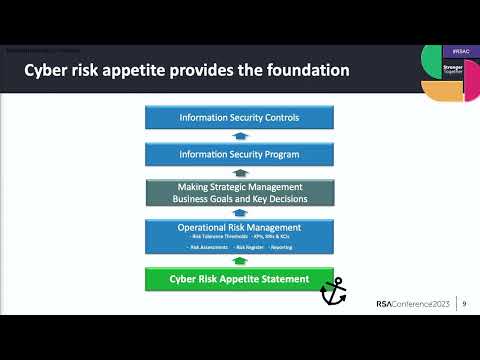
- 17:52Cyber risk appetite provides the foundation
- 20:04Cyber-related risk appetite guidance
- 22:4412 CFR Part 30 risk appetite guidance
- 23:55The Board owns the risk appetite
- 26:31Cyber risk appetite adherence reporting
- 28:07Risk appetite development principles
- 31:09Risk appetite communication practices
- 32:47The information security metrics quandary
- 35:38Risk appetite tolerance measurement & thresholds
- 40:25Cyber risk appetite tolerance development
- 42:20Example report #1 with thresholds
- 46:44Example: "ACMECo" cyber risk appetite statement
related talks
 28mHow to Tell the Right Cyber-Story to Executives and Board Members
 40mProtecting What Matters Most – Tools for Managing Risk
 15mFrom Risk to Return: Measuring Cybersecurity ROI with Data Analytics
 40mCybersecurity Metrics Development for Board and Risk Committee Reporting
 40mCyber Risk Management Programs: Bringing Clarity to Cybersecurity
 40mBuilding a Global Cyber Rating - How to Objectively Rate Cyber Capabilities
 47mTechniques to Evolve Risk Governance and Comply with SEC Cybersecurity Rule
 52mCybersecurity as a Business Conversation