Scaling Software Supply Chain Source Security in Large Enterprises
summary
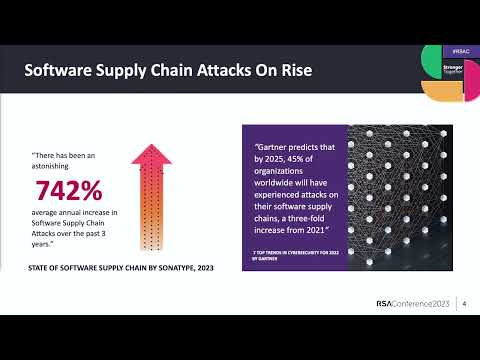
Large enterprises juggle open‑source, vendor, SaaS, hardware and internal chains and must catalog ingestion points, secure CI/CD and build systems, and monitor sources; use SLSA, NIST SSDF, SPDX/CycloneDX/SWID SBOMs and SCA tools; combine comprehensive queryable bill-of-material stores with VEX to filter exploitable CVEs so teams patch only truly impacted components; surprising data point: about 60–70% of organizations still pull vulnerable Log4j packages, and Gartner predicts most firms will suffer a supply‑chain attack by 2025.
AI-written summary · about
chapters (8)
- 0:00Introduction and speaker intro
- 1:26What is software supply chain
- 10:41Enterprise supply chain complexity
- 18:41Strategies to secure supply chain
- 27:25Addressing different attack types
- 32:27Understanding SBOM and VEX
- 39:36Resources and next steps
- 40:47Q&A session
related talks
 39mOpen Source Software Supply Chain Security — Why does it matter?
 39mSoftware Supply Chain Security
 15mSoftware Supply Chain Security for those in a rush
 41mManaging the Risk of Software Supply Chain Attacks
 44mKeeping Your Software Supply Chain Healthy
 09mSecuring the Software Supply Chain with Open Source
 41mSupply Chain Armoring: Tools and Techniques for Open Source Projects
 14mSupply Chain Security, why should I care?