Exposure Management: The Rise of Proactive Cybersecurity Platforms
summary
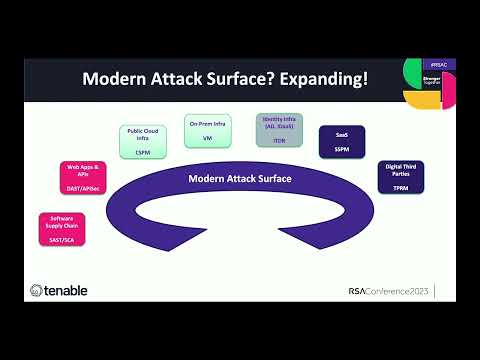
Argues for an exposure graph that links software, identity and devices to unify VM, CSPM, SAST/APISec, OT and identity scanners into one data platform; claims prioritization by combining exploitability, observed attacker usage and asset value into risk-based scoring; demonstrates instant Log4j inventory queries, finds 36 Chrome versions and five high‑privilege users with critical device vulns, and shows ServiceNow and EDR gaps feeding a federated CMDB. Calls this software-identity-device triangle for proactive, attack‑path prioritization.
AI-written summary · about
chapters (21)
- 0:00RSAConference 2023
- 4:43Modern Attack Surface? Expanding!
- 6:47Breaches Follow Weaknesses
- 11:05Operationalization
- 11:35Prioritization, Prioritization, Prioritization
- 11:45Practitioners Prioritization
- 13:33CISO Prioritization
- 14:17Threat Centric Prioritization
- 15:50Less Complexity
- 19:25Relationships: Context & Prioritization
- 22:37Example: Inventory rhymes with security
- 23:59Back to the Future: December 13th 2021
- 25:24Example: Identity Aware Exposure Mgmt.
- 28:27Gap in security controls!
- 29:38Continuous Control Monitoring
- 30:43Federated CMDB
- 31:23Back to the Graph: All you need is context...
- 35:03Open Approach Required
- 35:34Beyond Consolidation
- 36:05The Last Cyber Platform
- 36:27Next Steps: Exposure Mgmt. As Easy as 1-2-3
related talks
 12mCloud security: A critical part of your exposure management program
 26mExposure Management: The New Cyber Risk Strategy
 16mCyber-Exposure—The Next Frontier
 20mEvolving from patch management to risk mitigation
 58mCloud Attack Surface Management
 43mThe Art of Vulnerability Management - Practical Application of Cyber Triage
 26mProduction Is the New Attack Surface: Why Post-Deployment Endpoint Detection Is Now Critical
 38mCyber risk management: Bringing security to the boardroom