Securing the Software Supply Chain with Open Source

summary
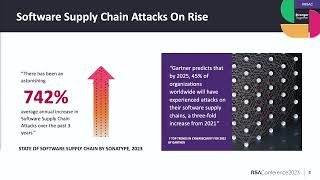
Open source runs nearly everything (90–98% use open source) and apps pull in many dependencies (135 components average), and supply‑chain attacks spike (surveys report 430–650% increases). The community assembles concrete tooling and standards: OpenSSF and the SLSA/salsa framework (SLSA levels 1–4 at slsa.dev) plus CI/CD and provenance projects aim to harden builds. Core operational advice: treat build infrastructure with the same security as production.
AI-written summary · about
related talks
 39mOpen Source Software Supply Chain Security — Why does it matter?
 11mSupply Chain Cybersecurity
 29mSecuring the Unseen: Defending Against Open Source Software Supply Chain Attacks
 07mHow to Secure Your End-to-end Supply Chain
 41mManaging the Risk of Software Supply Chain Attacks
 49mScaling Software Supply Chain Source Security in Large Enterprises
 32mWhy You Should Care About Open Source Supply Chain Security
 30mSecuring the Open Source Software Supply Chain