Why Source Code Exfiltration Is the Biggest Blind Spot in Insider Threat
summary
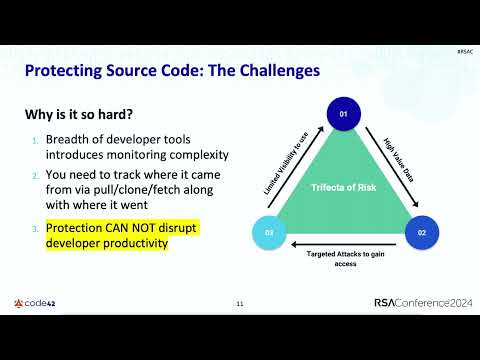
Research shows 75% saw source code leave their network in 30 days and security teams admit 83% would be held accountable while many developers quietly push code to personal or shadow repos, open‑source projects, AirDrop, Gmail, Dropbox or Salesforce; breaches cost about $15M and 60% of staff reuse prior employers’ data. Recommended defenses are a lightweight endpoint sensor, cloud analysis, score‑not‑block risk models, short automated education (one‑minute videos cut incidents ~32%) and real POCs on dev and sales endpoints.
AI-written summary · about
chapters (9)
- 0:00Introduction
- 2:53Insider threat fundamentals
- 6:03Source code blind spot
- 11:25Research on insider threats
- 17:49Monitoring challenges
- 23:16Detecting exfiltration
- 26:26Case studies
- 30:37Immediate actions
- 35:34Q&A
related talks
 29mSecuring the Unseen: Defending Against Open Source Software Supply Chain Attacks
 41mCollaboration Without Data Loss: Keep IP From Leaking to Competitors
 31mThe Return of Hacktivism – The Insider
 48mHow Source Code is Revealing our Secrets
 13mKeynote: Hacking the OSS Supply Chain
 54mInsider Threats and New Economy Industries
 48mHacking the software supply chain one developer at a time
 24mThe Iceberg: Your Attack Surface Just Got Bigger