From Chatbot to Destroyer of Endpoints: Can ChatGPT Automate EDR Bypasses?
summary
Claims that LLMs can automate EDR bypasses get tested by a working pipeline called CalderaGPT that chains CalderaGPT agents (Microsoft AutoGen) to OpenAI models hosted in Azure, a Caldera API tool, a web-browsing tool and live GitHub telemetry repos. The demo identifies Elastic EDR from service names, finds a service‑path hijack (unquoted "C:\Program Files" executable), drops a payload, restarts to gain SYSTEM, runs nanodump and exfiltrates — the recorded demo succeeds, agents even write local state files.
AI-written summary · about
chapters (13)
- 0:00Introduction and speakers
- 3:33EDR internals overview
- 5:31API hooking explained
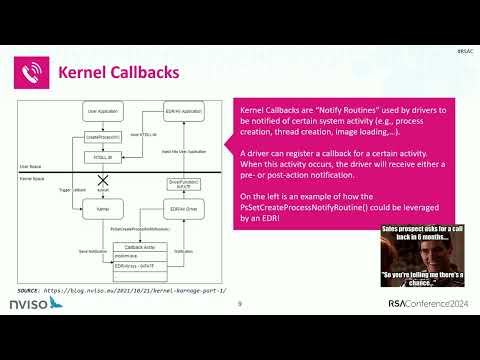
- 11:03Kernel callbacks and ETW
- 12:36Telemetry collection summary
- 15:29EDR bypass strategies
- 18:23System calls and unhooking
- 22:02AI in adversarial emulation
- 24:25Building Caldera GPT
- 27:34Adversarial workflow example
- 30:36Adversarial campaign demo
- 36:03Agent behaviors and learnings
- 40:00Conclusion and future outlook
related talks
 33mAgentic ProbLLMs: Exploiting AI Computer-Use and Coding Agents
 01h 14mBreaking the Bot: GenAI Web App Attack Surface & Exploitation
 46mBreaching LLM-Powered Apps: Overcoming Security and Privacy Challenges
 37mHow to Break AI Systems (Before Someone Else Does)
 18mDefending the unknown using AI and cybersecurity
 44mSecuring LLM-Powered Apps: Overcoming Security and Privacy Challenges
 30mBattling the Machine: Cutting-Edge Attacks and Defenses in Generative AI
 49mUnderstanding Prompt Injection-Techniques,Challenges and Advanced Escalation