The Unpatchables: Credential Stuffing Quantification and Classification
summary
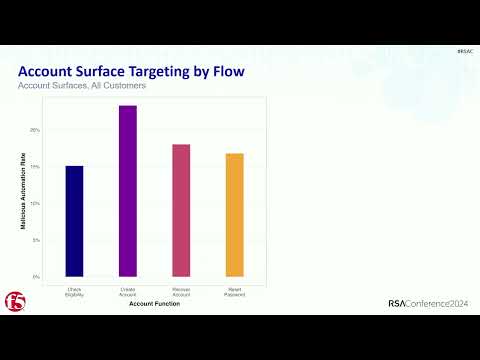
Analysis of more than 300 billion transactions shows credential stuffing constitutes about 20% average pre-mitigation traffic across 159 aligned customers and drops to ~6.4% after blocking. Attacks range from basic cURL/wget/SentryMBA bursts to intermediate token‑replay cases (52 million logins, 36 million unique accounts, 200k IPs, 1 token) and advanced Selenium/Puppeteer/Browser Automation Studio fleets. Telco, tech, travel and media see the most targeting; defenders note large use of canary accounts and recommend moving to WebAuthn/FIDO2 for MFA.
AI-written summary · about
chapters (15)
- 0:00Introduction
- 1:24Unpatchables in cybersecurity
- 3:47Credential stuffing attacks
- 5:56Measuring prevalence
- 8:32Mobile vs web traffic
- 10:19Targeted sectors
- 11:42Account management attacks
- 14:50Attack sophistication levels
- 20:35Advanced evasion techniques
- 26:32Canary accounts
- 29:23Compromised credentials visibility
- 31:05Key takeaways
- 35:39MFA bypass recommendations
- 38:05Q&A bot detection
- 40:32Q&A telco anomalies
related talks
 41mThe State Of Credential Stuffing And The Future Of Account Takeovers
 29mBecoming You: A Glimpse Into Credential Abuse
 41m📙 The Great Credential Caper: How to Perform and then Defend Against the (Nearly Impossible) to Defend 🏗️
 26mIntegrating Identity and Fraud
 16mProtecting your application from bot attacks (PRT019)
 40mWeb Attacks and Fraud: Lessons Learned from the Deep End of the Pool
 40mYou have a security problem - your users
 31mLog In Through the Front Door: Automating Defense Against...