Securing Cisco's Supply Chain - Cyberattacks and Intellectual Property Loss

summary
Cisco says over 80% of networking gear relies on its hardware and its supply chain handles 1.5 million orders last year across 600+ suppliers and 143,000 components. Risk work uses a likelihood×impact rubric, a master security specification and annual audits to score suppliers; an IP program uses a nine‑step pipeline with DLP (people/process/tech), backups and ROT elimination; anti‑counterfeit uses an immutable trust anchor TAM chip with a SUDI certificate baked at manufacturing plus secure boot and continuous runtime checks.
AI-written summary · about
chapters (15)
- 0:00Cisco supply chain security intro
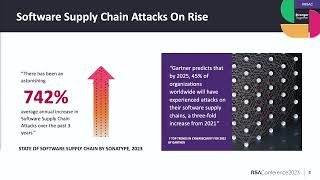
- 1:52Threat landscape for supply chains
- 4:06IP theft and counterfeiting risks
- 6:46Cisco supply chain security program
- 7:30Asset value and risk assessment
- 9:43Risk scenarios and registry process
- 11:35Third-party audit specifications
- 13:22Nine-step IP protection program
- 15:38IP protection strategy summary
- 17:06Anti-counterfeit technical controls
- 21:47Secure boot and runtime integrity
- 23:34Additional security initiatives
- 26:51Emerging challenges and future outlook
- 30:04Key recommendations for supply chains
- 32:33Q&A
related talks
 30mTaking Control of Cyber-Supply Chain Security
 49mScaling Software Supply Chain Source Security in Large Enterprises
 39mSoftware Supply Chain Security
 25mSupply Chain Attacks
 51mThe Enemy Within: Modern Supply Chain Attacks
 14mSupply Chain Security, why should I care?
 30mSupply Chain Security for IoT Devices
 26mCyber Resilience: Understanding Supply Chain Risks