Navigating M&A Security Challenges: A Deep Dive into a Case Study
summary
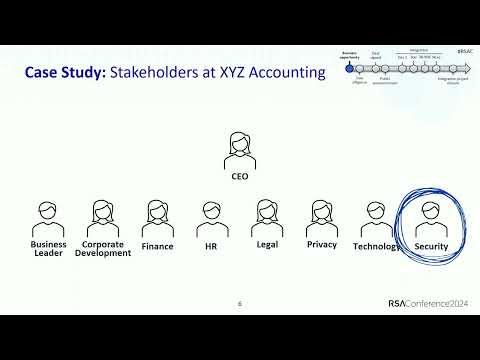
Case study follows a four-week due diligence on a 15,000-employee acquirer buying an eight-country target, using a cybersecurity rating, internal threat intel, a third-party SCA and static code review (executive summary only), a virtual physical tour, and an accepted vendor pen-test report. Target refuses a compromise assessment so teams agree a post-acquisition compromise assessment tied to price. Findings include no VPN MFA, end-of-life servers, high-severity code and pen-test issues, no formal third-party risk program and stale security training; day-one action is rapid agent deployment plus a 30/60/90 remediation plan.
AI-written summary · about
chapters (18)
- 0:00M&A security risks intro
- 2:10Key acquisition security risks
- 3:16M&A process and due diligence
- 4:23Case study XYZ Account Services
- 6:33Security due diligence challenges
- 10:27Due diligence gaps identified
- 14:03Post-acquisition integration
- 19:21Day one integration priorities
- 24:50Long-term risk management
- 27:39M&A security lessons summary
- 31:34Q&A on divestitures investments
- 34:04Due diligence costs translation
- 36:55Mergers ventures strategies
- 39:24Cultural differences in security
- 42:15Due diligence time pressure
- 45:23Due diligence vs integration
- 48:12Insider threat management
- 49:20Closing remarks Q&A
related talks
 30mSecuring Your M&A Activity with Cybersecurity Due Diligence
 43mAvoiding the Four Biggest Mistakes That Will Blow Up an M&A
 20mM&A Process pt.1
 44mCybersecurity - Protecting the Organisation's Technological Assets
 41mAim-Ready-Fire
 27mSmall Company, Big Threats: Cybersecurity for the Rest of Us
 50mCase Study: 10 Steps to Agile Development without Compromising Enterprise Security
 41mSecurity Touchpoints When Acquiring Soft...