MariaDB Roles
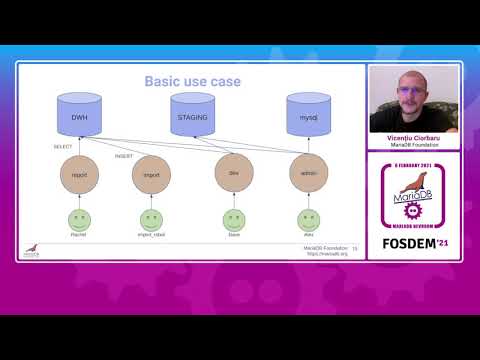
summary
Roles implement the SQL standard and MariaDB adds DEFAULT ROLE so legacy apps gain role rights on connect; grants form a directed acyclic role graph (MariaDB forbids cycles, MySQL allows them). Effective privileges are precomputed at server startup and cached, with system storage in mysql.global_priv and edges in mysql.roles_mapping. Migration from MySQL 8.0 requires mariadb-dump using the --system and user switch to emit CREATE ROLE/USER statements, but some MySQL privileges need manual mapping.
AI-written summary · about
chapters (8)
- 0:00Introduction to MariaDB Roles
- 3:54Role-based access example
- 6:24Role hierarchies and inheritance
- 8:46Performance and caching in roles
- 11:09Least privilege principle with roles
- 13:06Differences between MySQL and MariaDB
- 16:38Migration from MySQL to MariaDB
- 18:42Closing and Q&A
related talks
 34mUsing Roles and Partial Revokes To Improve Security in MySQL 8.0
 24mTips and Tricks for Migrating from Oracle to MariaDB
 41mMariaDB The New MySQL
 53mMariaDB Server 10.2: The Complete Guide
 41mState of MySQL Security in 2021
 21mSwitching from MySQL/Percona to MariaDB
 47mUntangling the Web of PostgreSQL Permissions
 47mOn the past, present and future of Open Source databases