Security Policy Management in the Hybrid Cloud
summary
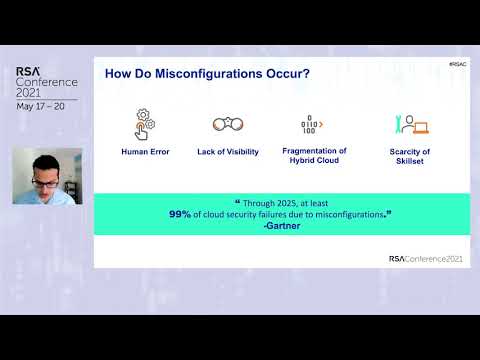
Companies face 81% cloud adoption while 72% report cloud security concerns and most breaches trace to misconfigurations. A centralized security policy management system that ingests on‑prem, multi‑cloud, Kubernetes, IAM and API gateway data, enforces vendor‑neutral policies, and injects shift-left policy checks into CI/CD automates policy delivery, removes manual key/config steps, and avoids adding firewalls to every VPC. Early adopters report faster migrations and fewer misconfigurations when the tool provides full east‑west visibility and actionable violations.
AI-written summary · about
chapters (10)
- 0:00Intro
- 0:40Business Goals
- 2:12Security and Agility
- 3:33Security Challenges
- 4:46Misconfigurations
- 9:37Lack of visibility
- 14:45Cloud complexities
- 25:13Summary
- 28:26Take away
- 30:32Outro
related talks
 28mSecuring Multi-Cloud and Hybrid Environments
 31mA Comprehensive Approach to Cloud Security Posture Management
 39mProtecting your hybrid cloud with Zero Trust
 31mAccess Policies for Hybrid Cloud Environments
 50mArchitecting a secure cloud framework
 58mCloud Attack Surface Management
 48mIt's an application-first world: Shouldn't your cloud security match? (PRT202)
 30mThe Next-Gen Elephant in the Room