Beyond Endpoints: A Case for Open XDR

summary
Security stacks stay scattered and costly so the argument is for an open XDR approach that centralizes and normalizes telemetry across vendors, applies prebuilt tuned correlation for ~70% of alerts that are repeatable use cases, and runs analytics for unknown threats. The vendor-led model pushes for 63% of top teams prioritize interoperability and 73% use automation across detection, investigation, and response. Practical examples include Sigma/STIX/MITRE formats, plug‑and‑play integrations, and automated responses such as forced password resets and containment actions.
AI-written summary · about
chapters (11)
- 0:00Intro
- 0:34Why XDR
- 2:28Disconnected tools
- 4:22Automation and integration
- 7:39Common practices
- 8:21What is XDR
- 11:14Open XDR
- 16:35Open ends with integration
- 19:40Open XDR in practice
- 22:02The value of Open XDR
- 23:23What to do next
related talks
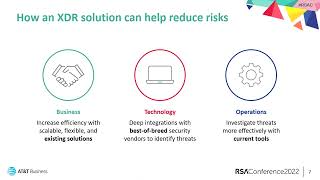 47mOpen XDR: A Strategy for Evolving Security Needs
 41mCutting Through the Noise of XDR – Are Service Providers an Answer?
 43mMaking Sense of a Confusing Detection and Response Solutions Landscape
 50mWhy Extended Detection and Response (XDR) Must Unite the Industry
 19mDefender XDR in the Real World: Measurable Risk Reduction
 24mThreat Response Needs New Thinking. Don't Ignore This Key Resource.
 12mSecurity data gravity: Visibility & threat detection for data lakes
 11mCybersecurity for an Inclusive Future