Building Cyber Resilience - Considerations for CISOs

summary
Banking systems with 15 million customers and oil infrastructure supplying 93% of national income face widening attack surfaces from cloud, OT/IT convergence and edge 5G/IOT; defenders report SOCs ingesting billions of events and use ML/RPA to triage but keep humans for major incidents. Practical takeaways: measure resilience (resilient-factor scoring, RTO/RPO), run joint drills, harden high‑value assets, insist on defense‑in‑depth and vendor controls after supply‑chain shocks (two‑thirds of breaches involve third parties).
AI-written summary · about
chapters (17)
- 0:00Introduction
- 4:43How NBBE is transforming its cyber resilience program
- 8:35How to define cyber resilience
- 12:48Importance of collaboration
- 13:53Telecommunications sector
- 19:28Aviation sector
- 23:28Resilience factors coding
- 24:33SolarWinds
- 26:53Supply chain attacks
- 28:18Emerging technologies
- 34:18Supporting the Cyber
- 38:08Collaboration
- 41:28Information Sharing
- 42:38Communication
- 43:38Checklist approach
- 44:28Key takeaways
- 46:58Power of 3
related talks
 45mBuilding Your Roadmap to Cyber Resilience – Five Things You Can Do Today
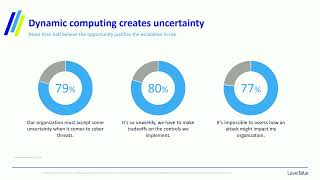 45mNew Research Reveals Five New Trends for Cyber Resilience
 54mThe Human Impact of Cyberattacks: Reframing the Defender Role
 22mFrom Risk to Resilience: How Security Can Shape the Future of Fintech
 50mManaging Cyber Risk to Systemically Important Critical Infrastructure
 49mHow to Create a Breach-Deterrent Culture of Cybersecurity, from Board Down
 56mSpanning the Globe: The State of the Industry from the People Who Run It
 22mCybersecurity: The Challenge of Our Decade