Attack & Defend: Protecting Modern Distributed Applications and Components
summary
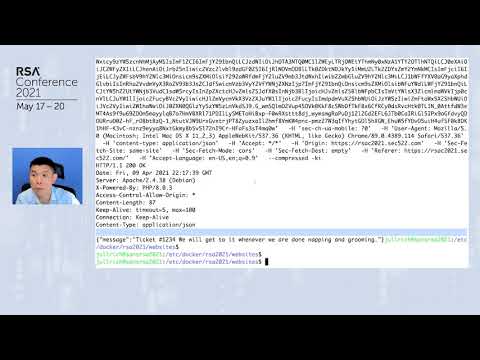
Browser devtools + curl reveal a JWT sent to the app; copying that token and posting it to the backend port (bypassing the Kong gateway) returns the same data, proving back ends accept bearer tokens directly. Certificate transparency and port scans expose alternative hostnames to target. Decoding the token on jwt.io shows roles that enable hidden API endpoints. Compromised CDN JS can steal keystrokes, but enforcing subresource integrity, private endpoint policies (source VPC), gateway-only token exchange, rate limits and gateway-side caching blocks these attacks.
AI-written summary · about
chapters (9)
- 0:00Introduction
- 1:33Application Architecture
- 4:07Microsurface Exposure
- 13:32Private Endpoint Policies
- 17:20Demo
- 23:15How to Defend
- 26:44Architecture
- 28:09Attack
- 34:54Lessons Learned