Securing Multi-Cloud and Hybrid Environments

summary
Claims concrete practices: unified security policies across providers, AWS Key Management Service or customer-managed keys for encryption at rest, TLS 1.3 for encryption in transit, mandatory multifactor authentication and role‑based access instead of long‑lived keys, network segmentation with Transit Gateway and Direct Connect for hybrid links, observability via Grafana/Splunk and ServiceNow asset tracking, regular audits and third‑party reviews to catch misconfigurations and prove compliance.
AI-written summary · about
chapters (7)
- 0:00Introduction
- 1:32Multi-cloud vs hybrid architectures
- 5:51Security challenges
- 12:44Security strategies
- 18:02Hybrid security models
- 22:17Data protection & compliance
- 26:14Summary
related talks
 21mCentralized security analysis in hybrid & multicloud with partners
 53mAchieving End-to-end Security on AWS
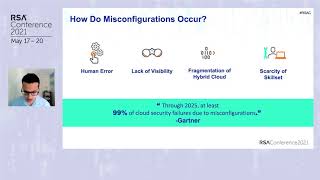 40mSecurity Policy Management in the Hybrid Cloud
 17mCloud Security in Continuous Delivery
 29mSecuring the Cloud: Multi-Layered Protection for Enterprises
 01h 09mCloud Safeguarding: View from Cloud Providers
 50mArchitecting a secure cloud framework
 31mA Comprehensive Approach to Cloud Security Posture Management