A First Look at Governments' Enterprise Security Guidance
summary
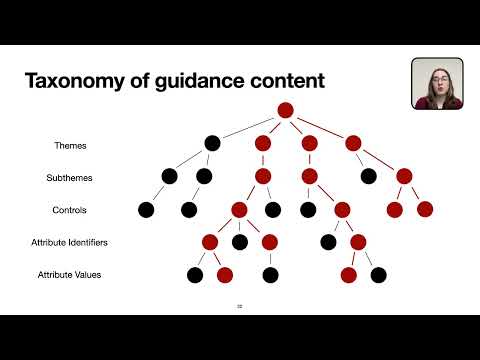
A systematic corpus of guidance from 41 countries is curated and represented with a tree-based taxonomy and a quantitative comparison metric, then ten “essential” documents are analyzed. Findings: only two unanimous controls: backups and patching, just 3% of controls appear in ≥75% of countries, Five Eyes members agree on only 13% of covered controls, many unique or peculiar recommendations appear (including a US pizza party recommendation), and several countries give directly contradictory implementation details.
AI-written summary · about
chapters (7)
- 0:00Government security guidance intro
- 1:15Research questions
- 3:01Global guidance scope
- 5:27Essential security controls
- 9:17Lack of consensus on themes
- 11:42Contradictions in controls
- 14:08Implications and future research
related talks
 32mThe One About Controls
 43mThe Hacker's Guide to Policyland
 01h 12mSecuring cyber critical infrastructure.
 53mOpen by Choice, Sovereign by Design
 40mSovereignty Spotlight: EU Regulations and the...
 44mCloud Security Essentials
 52mThe Hacker's Guide to Cloud Governance
 40mTotal Security: Investigative Perspectives from Public to Private Sector