Next-Level DevSecOps: Secure Supply Chain Consumption Framework Q&A

summary
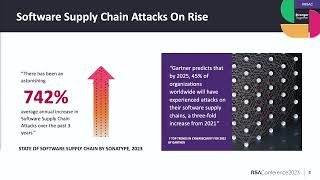
Microsoft presents the Secure Supply Chain Consumption Framework as a four‑level maturity model that maps to NIST, SSDF and other standards and targets developer consumption of OSS (NPM, NuGet, Maven, PyPI, crates, gems). It cites a 742% annual rise in OSS attacks and 88,000+ malicious packages, recommends Azure Artifacts + upstreaming, automated patching via Dependabot or Renovate, SBoMs and VEX files for transparency, and enforces policies that fail the build on insecure package sources; level 4 (rebuild everything) remains largely aspirational.
AI-written summary · about
chapters (4)
- 0:00Session introduction
- 2:55Understanding S2C2F
- 14:16Maturity model and adoption
- 19:34Q&A and best practices
related talks
 52mIntroducing the Secure Supply Chain Consumption Framework (S2C2F)
 51mOSS Supply Chain Threats and Why You Need a Holistic Security Strategy
 41mManaging the Risk of Software Supply Chain Attacks
 33mWhat is the secure software supply chain
 40mPractical guides for enhacing your Software Supply Chain Security
 49mScaling Software Supply Chain Source Security in Large Enterprises
 39mSoftware Supply Chain Security
 29mWe're All Consumers (And That's Dandy)