Shifting Authentication at Scale
summary
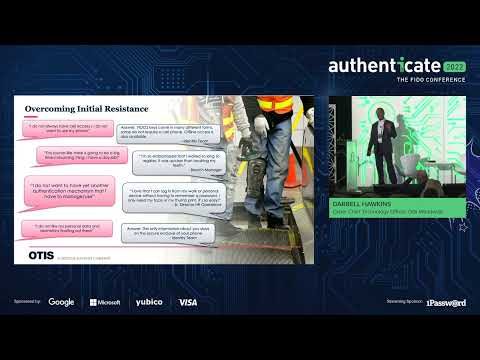
Otis replaces passwords for 41,000 employees across 200 countries by integrating a Hypr magic link passwordless MFA with identity governance (IGA) APIs, moving from a managed cert service to self-signed ADCS certificates, and creating synthetic identities to avoid email licenses. Onboarding time drops from weeks to 15 minutes, privileged access and apps like Workday and ServiceNow gain SSO, and field-worker device diversity drives a corporate-standard device policy. Deployment is completed by a single operator in a one-year global rollout.
AI-written summary · about
chapters (9)
- 0:00Introduction and speaker welcome
- 1:03Passwordless migration at Otis
- 3:33Onboarding challenges and infrastructure
- 6:26Business partnership and ROI
- 8:54Roadmap and global rollout
- 10:19Overcoming resistance to change
- 13:32Finding champions and communication
- 15:37Addressing cultural barriers
- 17:22Benefits and user experience
related talks
 30mWhere we’re going… we won’t need passwords
 49mGoing Passwordless for Employees: Secure Modern Authentication at Work
 23mBalancing enhanced security with excellent user experience in the enterprise
 25mNavigating the implementation and roll out of passwordless authentication
 22mWorkforce FIDO2 Orchestration Lessons Learned From Millions of Issued Credentials
 20mBeyond Passwords: A Journey to Seamless Authentication for Enterprise Software
 28mBuilding Identity for an Open Perimeter
 28mLessons From a Financial Services Passkey Deployment