Egalitarian Computing
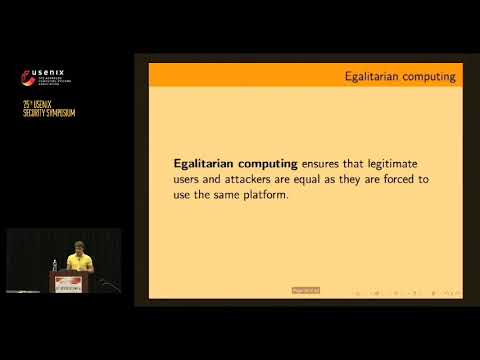
summary
Claim: making core operations brutally memory‑heavy removes ASIC energy and cost advantages so attackers lose the 30,000× Bitcoin-style edge. Implementation: use Argon2 as the memory‑hard primitive, build a fast‑verify memory‑hard PoW called MTP with 700 MB proofs compressed to ~120 bytes, and a memory‑hard encryption idea MHE that forces trial decryption to require hundreds of MB–GB of RAM (e.g., 2 GB → ~1 s), preventing cheap offline brute force and restoring laptop‑level competitiveness.
AI-written summary · about
chapters (4)
related talks
 20mEnabling Low-Cost Secure Computing on Untrusted In-Memory Architectures
 01h 23mProgram Presentations
 01h 08mSecure Computation 1
 01h 06mOblivious RAM II
 41mMiguel de Vega, Ravital Solomon, Remi Gai & Pascal Paillier I Pragma Denver 2024
 15mMAGE: Nearly Zero-Cost Virtual Memory for Secure Computation
 37mPETs of the world unite! Conquer the middle ground in the performance vs...
 42mPassword Hashing