Making USB Great Again with USBFILTER
summary
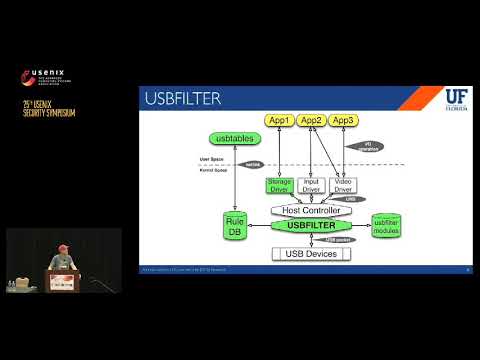
Kernel-layer USB firewall that mediates every USB packet by sitting between drivers and the host controller, tracing packets back to PIDs and enforcing policies from a user-space Prolog tool called usbtables. Implements packet-level access control and can restrict interfaces to a particular application (e.g., only Skype may use a webcam). Prototype touches 27 kernel files (4 new, 23 modified), offers ~20 rule primitives, adds ~2.6 μs per-packet filtering and ~5.9 ms rule-add latency, and blocks HID/storage misuse in evaluated workloads.
AI-written summary · about
chapters (18)
- 0:00Intro
- 0:48Why USB was great
- 3:31USB enumeration
- 4:31USB device
- 5:32USB packet
- 7:51Goals
- 9:21Rule constructions
- 10:32Rule consistency
- 12:23Linux USBFILTER Module (LUM)
- 13:06LUM: detect the SCSI write cmd
- 14:55Stop BadUSB attacks
- 15:34Pin Skype to webcam
- 16:11Stop data exfiltration
- 18:35Scalability
- 21:00Latency
- 22:13Limitations & Future Work
- 25:06Conclusion
- 28:05Charge safe
related talks
 27mUSBGuard
 36mUSB Arsenal for Masses
 25mDon't Trust Your USB! How to Find Bugs in USB Device Drivers
 18mμUSB: Practical and Safe USB Driver Reuse for Arm TrustZone
 52mDebugging Usually Slightly Broken (USB) Devices and Drivers
 27mCracking With Automated USB Fuzz
 26mUSB Snooping Made Easy: Crosstalk Leakage Attacks on USB Hubs
 45mBadUSB - On Accessories that Turn Evil