Asymmetric Encryption: A Deep Dive

summary
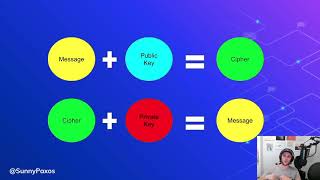
Starts with a concrete RSA worked example using primes 17 and 19 so n = 323, Carmichael λ = 144, public exponent e = 5 and private d = 29 to show why modular exponentiation recovers plaintext; builds an elliptic curve over Z11 with equation y^2 = x^3 + x + 5 mod 11 and demonstrates point addition and a generator sequence; explains how Shor finds period r = 48 to factor 323 and thus breaks RSA and elliptic discrete logs; surveys production post‑quantum choices like CRYSTALS‑Kyber and DILITHIUM and notes Chrome and Cloudflare experiments.
AI-written summary · about
chapters (17)
- 0:00Asymmetric encryption intro
- 1:21Cryptography history
- 5:54Why asymmetric crypto matters
- 6:59How RSA works
- 11:13RSA example
- 15:04RSA limitations
- 18:13Group theory basics
- 24:52Elliptic curves role
- 29:50How elliptic curve cryptography functions
- 35:50Advantages of elliptic curve over RSA
- 36:32Quantum threat Shor's
- 39:01Shor's breaks RSA
- 42:11Post-quantum solutions
- 46:04Kyber Dilithium algorithms
- 47:49Implementing post-quantum crypto
- 49:33Future crypto risks
- 51:17Summary
related talks
 58mAsymmetric Encryption: A Deep Dive
 40mAsymmetric Encryption: A Deep Dive
 56mAsymmetric Encryption: A Deep Dive
 46mFrom substitutions to public keys - an introduction to cryptography
 15mRSA encryption in 10 minutes
 01h 26mTLS Cryptography for Programmers
 01h 00mCS Fundamentals: Why SSL and SSH are Secure
 29mHow Prime Numbers Keep the Internet Secure