CS Fundamentals: Why SSL and SSH are Secure

summary
Shows working code that implemented a one-time pad in C# and warns never to roll your own crypto; demonstrates modular math and generated primes and semiprime n (slow with naive BigInteger loops) to form RSA keys; performs Diffie‑Hellman to derive a shared secret and uses RSA to encrypt a small numeric message (decryption succeeds for test primes); notes historical surprise that RSA‑129 is cracked in 17 years not 40 quadrillion and flags quantum computers as a future threat.
AI-written summary · about
chapters (22)
- 0:00SSL and SSH security intro
- 1:48Cryptography history importance
- 3:53Encryption and decryption
- 4:56Caesar Cipher and keys
- 7:21One-time pad and math
- 9:31Live C# one-time pad
- 15:59One-time pad limits
- 16:42Breaking Enigma lessons
- 19:12Diffie-Hellman exchange
- 23:24Live C# Diffie-Hellman
- 29:53Diffie-Hellman impact
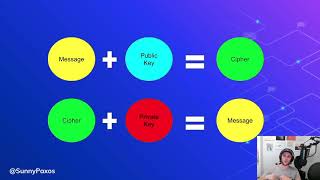
- 30:36Asymmetric encryption RSA
- 32:00RSA algorithm primes
- 35:55Live prime generation
- 44:50RSA encryption math
- 47:41RSA decryption math
- 51:20Live RSA encryption
- 52:46RSA with symmetric crypto
- 54:30Crowd-test RSA-129
- 56:57Breaking RSA future
- 58:43Quantum threat to RSA
- 59:47Conclusion cryptography
related talks
 46mFrom substitutions to public keys - an introduction to cryptography
 01h 26mTLS Cryptography for Programmers
 25mCryptography Isn't Scary
 58mKeynote: Crypto means Cryptography!
 40mAsymmetric Encryption: A Deep Dive
 29mHow Prime Numbers Keep the Internet Secure
 52mAsymmetric Encryption: A Deep Dive
 55mThe secrets of Cryptography