Community-led Security at ASF
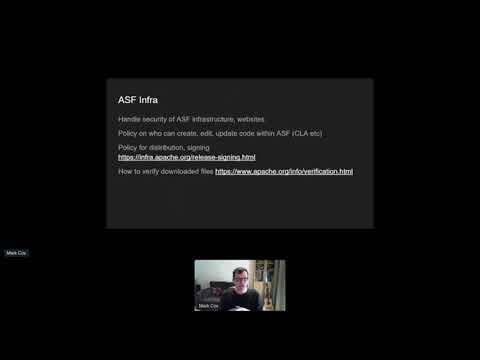
summary
Apache Security triages about 17,000 reports/year into roughly 1,000 threads and ~400 validated vulnerabilities, issuing about 150 CVEs/year via its CNA API and an internal tracking tool; today 87 issues span 40 projects with a median open time of 79 days. Projects sign releases with GPG, publish source-first artifacts, and face daily noisy dependency alerts from GitHub-centric scanners. Work underway includes OpenSSF scorecard, SBOM/criticality mapping, sigstore-style signing, and a new community security mailing list.
AI-written summary · about
chapters (12)
- 0:00Intro
- 0:24Welcome
- 1:16Executive Order Critical
- 2:30Security Committee
- 7:05Infrastructure Policies
- 8:06Consistency
- 9:16Why is this important
- 10:05NIST guidelines
- 10:23Code verification
- 12:29ASF
- 14:40CI Badges
- 15:38Third Parties
related talks
 44mSecuring Open Source Software - End-to-End, at Massive Scale, Together
 41mBack to Security Basics: Evaluating, Consuming, and Contributing Open Source...
 30mEffective Vulnerability Management for Over 400 Projects at the Eclipse Foundation
 48mImproving the Security of a Large Open Source Project One Step...
 31mA Glimpse Into OSS Vulnerability Disclosure Practices
 43mApplication Security is a Community Effort
 45mSimplifying Coordinating Vulnerabilities & Disclosures in Open Source...
 41mKeeping Up With The Joneses (CVEs)