Why and How We Updated Our License Policy for Use of Open Sou...

summary
Alliander's OSPO updates a sprawling 2020 license policy into a concise, one‑page license‑vs‑use‑case matrix that maps permissive, weak/strong copyleft, AGPL/network, source‑available and non‑commercial licenses against four real uses: code snippets, libraries, build tooling, and standalone apps. The policy keeps a linked, legal-reviewed license list and documents case evaluations, logs exceptions registered with legal, and flags surprising scale — about 30,000 libraries/month surfaced by scans — while planning automated scans and pipeline enforcement.
AI-written summary · about
chapters (14)
- 0:00Introduction
- 3:51Open source license policies matter
- 7:03Original policy challenges
- 10:53User-friendly license policy
- 12:20Updated policy components
- 16:34License-use case matrix
- 24:03Lessons from policy revision
- 27:56Closing and Aliander projects
- 28:39Q&A on policy awareness
- 32:13Legal department collaboration
- 35:02Security and privacy teams
- 36:28External policy collaboration
- 37:53Reusing license categorizations
- 40:02Q&A on Docker dependencies
related talks
 30mOpen Source Licensing: Use Versus Abuse
 14mOpen Source Licensing in a Business World
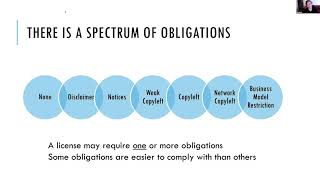 01h 38mOpen Source Licensing: Types, Strategies and Compliance
 32mSOS: Sustainable Open Source
 57mWhat You Need to Know About Open Source—Trust Me, I'm a Lawyer
 42mOpen Source Licenses: Between Parish Wars and Radicalism
 39mA decade of lessons in Open Source licensing
 48mWhat You Need to Know About Open Source - Trust Me, I'm a Lawyer