Are you using an opensource library?

summary
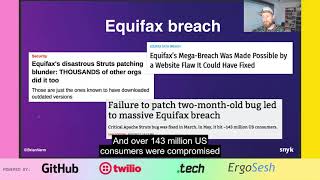
Many projects inherit vulnerable open‑source code and a single transitive dependency can enable full remote code execution. Examples: Apache Commons Collections and Struts led to the San Francisco MTA outage (≈2,112 systems) and Equifax (143M US, 44M UK records). A live demo uses Spark Java + Jackson ObjectMapper to exploit CVE-2017-7525 by deserializing a base64‑encoded payload into Jackson Databind TemplatesImpl, which runs its constructor on the server. Recommended defenses: CI/CD scanning with tools like Dependency-Check, update or replace libraries, and monitor transitive dependencies.
AI-written summary · about
chapters (19)
- 0:00Intro
- 1:47Twitter
- 2:02Agenda
- 6:59CRA hack
- 9:31Equifax hack
- 11:51Why opensource libraries
- 13:00Competitive advantage
- 14:20Dependencies
- 15:07transitive dependencies
- 15:26Sample project
- 16:04Vulnerabilities
- 16:47Inspection of Vertex
- 17:26Trust 515
- 17:46Trust 515 vulnerabilities
- 18:15Do hard choices
- 19:00Demo
- 20:11Spark Java
- 32:24Preventive measures
- 35:49Conclusion
related talks
 32mBuilding a secure future using DEVSECOPS practices and technologies
 46mAre We Ready For The Next Cyber Security Crisis Like Log4Shell?
 19mHow a vulnerability hack may happen and how to prevent it
 50mStranger Danger: Your Java Attack Surface Just Got Bigger
 48mCommon vulnerabilities you wish your Java app didn't have!
 39mWe Are All Equifax: The Data Behind DevSecOps
 56mThe Anatomy of Java Vulnerabilities
 18mLive Exploiting Your Open Source Dependencies