Common vulnerabilities you wish your Java app didn't have!

summary
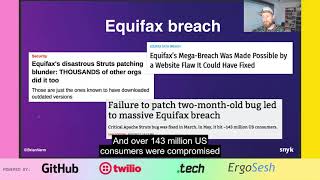
Counts and concrete exploits decide whether to watch: a 19-line Node app pulls 19 deps and deploys ~191,000 lines; a 222-line Spring app pulls dozens of libs and becomes ~500,000 lines. Real attacks shown: zip slip arbitrary file overwrite that replaces JDK tools, Jackson RCE via unmarshal on a Spring Cloud Function that returns /etc/passwd and executes commands, a regex backtracking DoS that hangs threads with 60,000 characters, a Spring Data REST RCE exposing env vars. Snyk scans and auto-PR fixes are demonstrated.
AI-written summary · about
chapters (13)
- 0:00Introduction to security session
- 1:08What is DevSecOps?
- 3:12Open source security risks
- 9:11Live hacking begins
- 12:43Directory traversal vulnerability
- 16:35Regex denial-of-service
- 20:35Spring Data REST exploit
- 24:53Jackson deserialization attack
- 33:27Cross-site scripting in Marked
- 39:17Zip slip vulnerability
- 43:14Tools and solutions for security
- 45:20Team culture and process changes
- 47:09Q&A and closing remarks
related talks
 01h 06mLive hacking: Breaking into your Java web app
 48mThe Hidden Security Hazards in Your Java Stack
 43mLive hacking: Breaking into your Java web app
 56mThe Anatomy of Java Vulnerabilities
 50mStranger Danger: Your Java Attack Surface Just Got Bigger
 46mLive hacking: Breaking into your Java web app
 40mLive hacking: Breaking into your web app
 18mLive Exploiting Your Open Source Dependencies