Live hacking: Breaking into your Java web app

summary
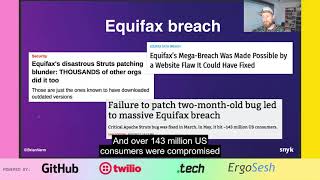
Live demos exploit Apache Struts RCE to run arbitrary OS commands on a Heroku instance (curl shows environment vars, /etc/passwd), a zip slip overwrite native2ascii attack that replaces the JDK binary to tamper uploaded titles, and a Spring Data REST expression injection that executes commands via PATCH. Examples run successfully against real libraries, cite Equifax’s 145+ million records, show typical apps pulling 400k+ lines of transitive code, note median 2.5 years to discover bugs, and finish with Snyk tooling (CLI and IntelliJ plugin) to detect and fix dependencies.
AI-written summary · about
chapters (11)
- 0:00DevSecOps and security mindset
- 3:00Siloed security in DevOps
- 5:23Security failures like Equifax
- 10:17Third-party dependencies risks in Java
- 17:40Path traversal in Node.js demo
- 22:11Zip slip file overwrite in Java
- 27:23Spring Boot SPEL vulnerability
- 33:18Security solutions: Culture, process, tooling
- 36:53Automating security with Snyk
- 40:25Shift-left security in development
- 42:52Secure Java development resources
related talks
 01h 06mLive hacking: Breaking into your Java web app
 40mLive hacking: Breaking into your web app
 46mLive hacking: Breaking into your Java web app
 01h 02mLive Hacking: Breaking into your Web App
 41mLive Hacking: Breaking into Your Web App
 18mLive Exploiting Your Open Source Dependencies
 52mDevSecOps
 47mLive Hacking: Breaking into Your Web App