dev.privacy: GDPR in a nutshell

summary
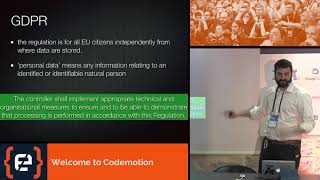
Practical GDPR steps for cloud services: map data flows, record purposes and retention, and prove consent while preparing for the right to be forgotten and backup challenges. Describes a real deployment with 1.5 million users, two data centers, ~100k files/day and 600 servers, using segregation of duties, hashing vs randomized tokens, and layered cryptography. Implements per-file symmetric keys encrypted with user public keys to achieve end-to-end encryption/zero-knowledge, and recommends incident detection testing, log heuristics and cross-department breach playbooks.
AI-written summary · about
chapters (30)
- 0:00Introduction
- 0:27About Evan
- 1:13About my job
- 2:04Turkey
- 3:22Crime
- 3:47Privacy is lost
- 4:26Privacy is our problem
- 4:37Safety belt
- 5:20What is GDPR
- 5:53Burden of proof
- 6:31Three kinds of data
- 7:05How to manage data
- 7:36Data storage
- 8:17Types of data
- 10:26How to inform the user
- 11:37Should I ask for explicit content
- 13:31Separate data
- 13:46Personal data
- 14:56Data integrity
- 15:57Right to be forgotten
- 17:22Cloud storage
- 17:46GDPR compliance
- 20:37cryptography
- 21:41encryption
- 23:36security
- 25:23plan
- 26:00detection
- 26:24cybersecurity
- 29:27data breach
- 31:28FAQ
related talks
 23mdev.privacy: GDPR in a nutshell
 23mCompliance Beyond Security: a Cloud Native GDPR Implementation Experience
 52mDeveloping privacy
 01h 00mPrivacy and GDPR: What all developers should know
 01h 59mDeep Dive Workshop – Data Security and Data Protection
 01h 59mDeep Dive Workshop – Data Security and Data Protection
 49mPractical privacy: GDPR explained
 23mThe GDPR impact in database project