CIAM for AI: Authn/Authz for Agents
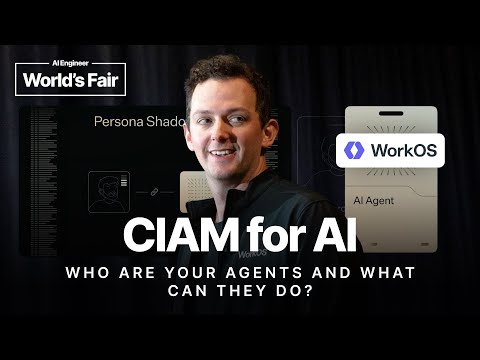
summary
Claims that agents need first-class, hybrid machine+person identities and that agent traffic will flip from ~5% to ~95%. Lists four practical patterns: persona shadowing, delegation chains, capability tokens, and human escalation, plus middleware between agent code and enterprise systems (WorkOS mentions OKIT and FGA). Calls out hard requirements: headless long‑lived sessions, dynamic least‑privilege, cryptographic delegation (GNAP, OIDC extensions, UMA, verifiable credentials), and enterprise logging/compliance to track fast, massively parallel agent actions.
AI-written summary · about
chapters (8)
- 0:00Introduction to CIAM for AI
- 1:04AI agents need identity
- 3:31Why agent identity is hard
- 6:19Architecture patterns for agents
- 10:52Emerging identity standards
- 15:21Middleware for agent security
- 17:05Future of agentic interactions
- 18:52Call to collaboration
related talks
 25mAgents Are Not Users or Services: Securing AI Traffic with a New Identity Model
 35mIdentity and Access Management for the Decade Ahead
 40mIn AI We Trust? Securing the Future, One Agent at a Time
 17mDon't give your agent the master key
 16mIdentity-Centric Security for AI Systems
 23mWho is Calling? Identity for Agents with AAuth
 01h 22mIdentity for AI Agents
 27mFrom Perimeter to Silicon: Why Agentic AI Demands a New Security Model