The State of Web Security
summary
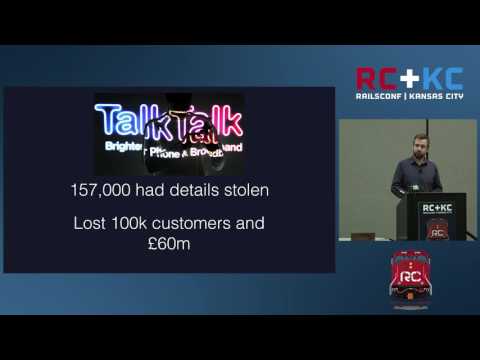
2015 breach data shows concrete harms: SQL injection still lets attackers exfiltrate millions (TalkTalk ~157,000 accounts, ~£60M loss; VTech = 200k kids + 5M parents; Wetherspoons ~650k and free beer) and credential dumps proliferate (866 million credentials). Rails-specific holes (CVE‑2016 render/absolute‑path file disclosure and earlier ERB execution) enable arbitrary file read/remote code exec; defenses discussed include SQL injection detection via query‑level checks and Runtime Application Self‑Protection (RASP) inside apps rather than brittle perimeter WAFs.
AI-written summary · about
chapters (8)
- 0:00Introduction
- 2:55The State of Web Security
- 4:36Whos Protecting Our Data
- 6:59SQL Injection
- 10:51Information Leak
- 14:53Render params
- 17:51Website ransomware
- 24:46How to protect yourself
related talks
 01h 30mCommon Webapp Vulnerabilities and What to Do About Them
 59mPractical Security for Web Applications
 59m50 Shades of AppSec
 57mLessons From Billions of Breached Records
 40mData Breaches: Barbarians in the Throne Room
 55mBreaking and Fixing Web Application Security
 47mEsoteric Web Application Vulnerabilities
 28mLearning from High Profile Failures