Secrets Management for the Modern Tech. Pro
summary
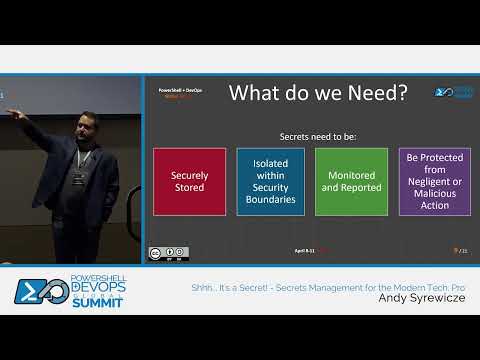
Hardcoded credentials get replaced with an automated flow that actually works: scripts create or use Azure Key Vault, push 22‑char random passwords, and retrieve secrets by URI; soft delete and purge protection prevent accidental loss; Key Vault firewall and just‑in‑time IP rules limit exposure; on‑prem servers register via Azure Arc and use a system-assigned managed identity to fetch tokens (Invoke‑WebRequest/Invoke‑RestMethod) so no username/password circulates. Real breaches (CISA, Uber) justify the ROI and the constraints.
AI-written summary · about
chapters (13)
- 0:00Secrets management intro
- 1:11Speaker intro
- 3:18Hardcoded secrets risks
- 9:21Consequences of exposed secrets
- 11:05Secure secrets requirements
- 14:39Azure Key Vault benefits
- 16:24Demo: Azure Key Vault setup
- 21:21Key Vault with PowerShell
- 25:59Secure password generation
- 30:15Chicken-and-egg auth problem
- 33:30Managed identities demo
- 43:15Security layers & considerations
- 44:40Q&A
related talks
 47mManaging your Secrets in a Cloud Environment
 10mCan you keep it a secret?
 44mSecrets at Scale: Managing Cloud Credentials with PowerShell Automation
 22mSecure your secrets with automation
 43mSecure Development
 29mBehind Closed Doors: Managing Passwords in a Dangerous World
 26mHow To Keep A Secret
 39mHow to steal Azure DevOps secrets