Understanding programmable system call security with Secomp-eBPF in Linux.
summary
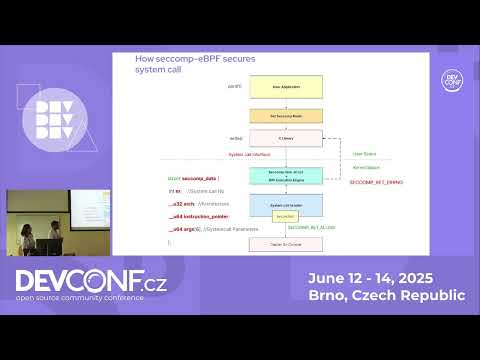
Demonstrates using eBPF + seccomp to compile and load BPF filters via prctl, observing that Linux exposes ~400 system calls and showing a working demo that blocks syscall number 3 (close) so running ls fails when close is denied. Shows filters run in-kernel through the eBPF verifier, return errors like -EPERM ("operation not permitted"), and prevents exploits that need execve, setuid, fork/clone or mmap (citing a WebKit arbitrary‑code CVE). Mentions bcc and bpftrace for profile generation.
AI-written summary · about
chapters (12)
- 0:00Introduction
- 1:03System calls and their role
- 2:07System call security necessity
- 3:10eBPF and its evolution
- 4:22eBPF accelerating kernel adoption
- 6:20seccomp and its purpose
- 7:04seccomp securing system calls
- 8:30Vulnerabilities mitigated by seccomp
- 12:21seccomp with eBPF integration
- 14:35Live demo blocking system calls
- 19:40Use cases of seccomp-eBPF
- 21:40Q&A
related talks
 01h 03mUsing seccomp to limit the Linux kernel attack service
 01h 29mUsing Seccomp to Limit the Kernel Attack Surface
 52mUsing Seccomp to Limit the Kernel Attack Surface
 35mRevisiting eBPF Seccomp Filters
 26mReinventing Seccomp for Fun and Profiles
 01h 21mTutorial: The Why and How of libseccomp
 42mResolving Performance and Security Issues with eBPF
 44mSeccomp for Developers - Making Applications Simply More Secure