Generate seccomp profiles for containers using bpf
summary
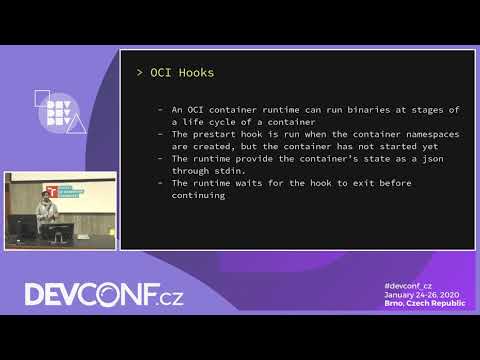
Generates per-container seccomp profiles by attaching an eBPF tracepoint sys_enter program and a short daemon launched via an OCI pre-start hook, recording syscalls only from the container’s PID namespace (compare to PID 1) after prctl indicates seccomp is applied. Prototype requires root/cap_sys_admin, produces a profile that tightened the default (default shipped profile leaves hundreds of calls; research says containers typically need ~60–70 calls), blocked extra calls in demos, supports merging an input profile for CI and showed minimal overhead.
AI-written summary · about
chapters (16)
- 0:00Seccomp and container security
- 1:27Standard seccomp profile issues
- 2:50Why ptrace and audit fail
- 3:52BPF and eBPF solution
- 5:59PID namespace process tracking
- 7:04OCI hooks for syscall monitoring
- 8:35Generating seccomp profile demo
- 10:40Testing and extending profile
- 12:41Original vs new profile comparison
- 14:05Runtime requirements and limits
- 15:12Q&A on container isolation
- 16:36Testing code path coverage
- 17:41Performance impact of eBPF
- 19:06Why static analysis fails
- 19:47Production deployment recommendations
- 20:07Conclusion
related talks
 39mCustom seccomp Profiles with Inspektor Gadget
 26mReinventing Seccomp for Fun and Profiles
 32mSecuring Kubernetes Applications by Crafting Custom Seccomp Profiles
 10mGenerating seccomp policies with eBPF
 40mUsing the EBPF Superpowers To Generate Kubernetes Security Policies
 15mTest-driven Hardening: Crafting Seccomp Profiles within Test Pipeline
 34mSeccomp: What Can It Do For You?
 52mUsing Seccomp to Limit the Kernel Attack Surface