How do I..? Answering common questions from RP devs
summary
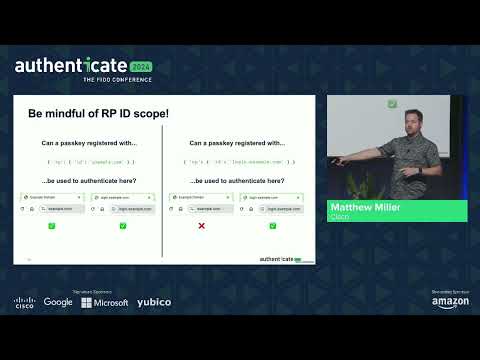
Explains three concrete new WebAuthn signal APIs — signal unknown credential, signal all accepted credentials, signal current user details — described as fire‑and‑forget calls browsers forward to authenticators or providers to hide or delete stale credentials and update metadata; describes RP ID scoping rules (root domain vs subdomain, excludeCredentials -> InvalidStateError to detect re‑registration), related Origins using .well‑known/webauthn to allow cross‑domain passkey reuse, iframe allow plus removing X‑Frame‑Options, and that browsers forbid IP hosts and cannot force biometrics over PIN.
AI-written summary · about
chapters (9)
- 0:00Introduction
- 1:48Pass keys on IP addresses
- 3:59Requiring biometrics only
- 5:02Deleting credentials
- 8:54Pass keys in iframes
- 10:19Skip registration for known keys
- 11:22RP ID scoping explained
- 13:30Related domains with pass keys
- 16:00Q&A session
related talks
 18mA Developers Guide to WebAuthn
 25mWebauthn; Don’t do it wrong when doing it right
 20mWebAuthn: The Revival of Authentication
 42mBeyond Passwords: How WebAuthn Actually Works
 30mWebAuthn Rocks! Stop authenticating as if it were the 60s
 40mWebAuthn 201: How to FIDO
 01h 14mWebAuthn: Theory and practice
 45mPasswords Are So 1990