Detecting Compromise of Synced Passkeys
summary
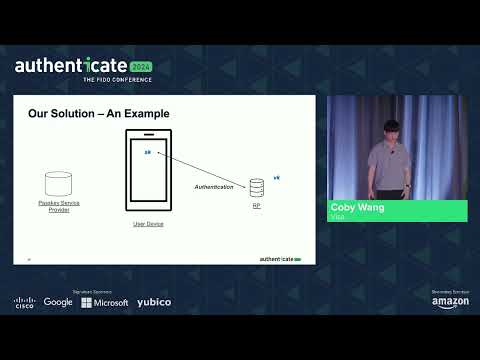
Proposes a deception layer that registers extra decoy verification key entries alongside the real passkey so attacker guesses can trigger alerts; prototype and analysis show deployment with low cost and no extra user friction. Uses low-entropy, recoverable secrets (minimum ~5 bits, e.g. short PIN) to derive many decoy keys; with 32 decoys the attacker trips a decoy with >95% detection probability while false alarms remain negligible.
AI-written summary · about
chapters (8)
- 0:00Introduction to authentication
- 1:48Passkeys and device binding
- 3:58Sync passkeys and trade-offs
- 6:25Post-breach detection approach
- 10:01Defense strategy with decoys
- 17:08Solution summary and benefits
- 18:31Passkeys future and conclusion
- 19:13Q&A session
related talks
 24mRelying Party Security
 30mAuthentication for humans, why passkeys finally make sense.
 52mPasskeys: The Good, the Bad and the Ugly
 52mPasswords are Dead, Long live Passkeys!
 38mPasswordless App with Passkey
 19mOSPEAD: Optimal Ring Signatures
 40mKeeping secrets in your opponent's hands
 14mPractical Attacks on a Decentralized Secure Messenger Session