Hack, Patch, Repeat: Insider Tales from Android’s...
summary
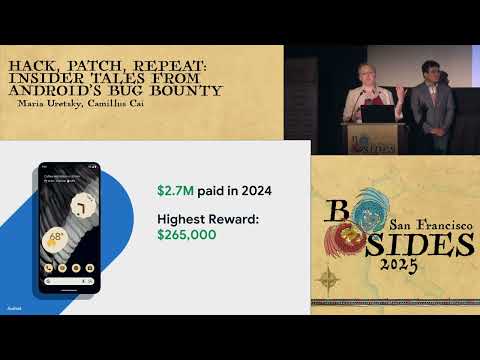
Shows how the Android VRP turns research into fixes: a 2023 Cropalypse uncrop exploit leads to a CVE and patch; a kernel HID bug that leaks addresses via Kmalloc gets fixed by switching to kzalloc to zero memory; programmatic trends drive design changes (Rust migration cuts memory-safety reports ~32%, background-activity mitigations halve abuse). Last year the program handles 2,157 reports and pays researchers ($2.7M in 2024) while prioritizing reproducible PoCs and exploit chains.
AI-written summary · about
chapters (7)
- 0:00Introduction and speakers
- 1:25What is Android
- 12:31Android security model
- 22:42Real-world vulnerabilities
- 29:02Bug bounty impact and trends
- 37:28Getting started with Android VRP
- 40:41Q&A and closing
related talks
 42mAndroid: Protecting the Kernel
 53mThe Art of Defense - How Vulnerabilities Help Shape Security Features and Mitigations in Android
 32mYear in Review: Android Kernel Security
 41mOverview of common Android app vulnerabilities
 33mOverview and Recent Developments: Kernel Self-Protection Project
 53mAndroid: He protec, but he also attac
 41mFive Years of Android Security Research: the Good, the Bad...
 47mAdaptive Kernel Live Patching: An Open Collaborative Effort...