KSG: Augmenting Kernel Fuzzing with System Call Specification Generation
summary
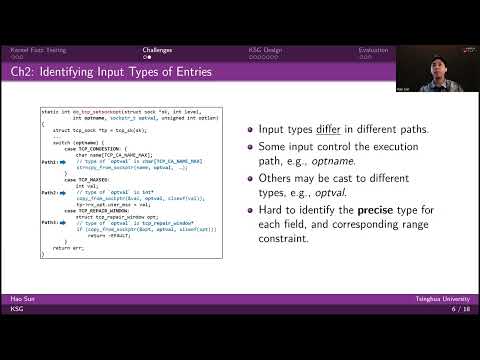
KSG automatically generates Syzlang system call specs by using eBPF/kprobe tracing to extract module entry points, then path-sensitive, symbolic analysis to infer per-path input types and range constraints and map them to Syzlang. It produces 2433 unique specs (about 1460 new to existing infra), feeds Syzkaller/Moonshine and yields 22% coverage improvement on average, and helps find 26 previously unknown bugs with multiple CVEs assigned.
AI-written summary · about
chapters (11)
- 0:00Intro
- 0:30Kernel Fuzz Testing
- 1:42System Call Specification
- 4:59Ch1: Extracting Entries of Submodules
- 6:17Ch2: Identifying Input Types of Entries
- 7:49Overview
- 8:46Entry Extraction
- 11:58Types and Constraints Collection
- 13:39Running Example
- 15:30Evaluation: Specification Generation
- 19:03Summary
related talks
 19mSYZOS: Practical KVM fuzzing
 43mSyzbot and the Tale of Thousand Kernel Bugs
 39mSyzDescribe: Principled, Automated, Static Generation of Syscall Descriptions for Kernel Drivers
 37mSyzbot: 7 years of continuous kernel fuzzing
 20mKFuzzTest: Targeted Fuzzing of Internal Kernel Functions
 38mHow I started chasing speculative type confusion bugs in the kernel and ended up wi...
 46mBypass Kernel Barriers: Fuzzing Linux Kernel in Userspace With LKL
 24mMoonShine: Optimizing OS Fuzzer Seed Selection with Trace Distillation