Protecting Encryption Keys with Azure Key Vault

summary
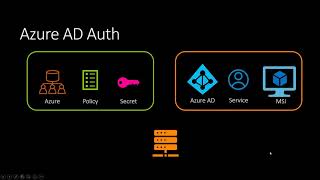
Step-by-step demo of Azure Key Vault: creates keys and secrets, calls AzureAD for app auth, and runs code that encrypts/decrypts, signs and verifies, and shows local key wrapping with an AES session key protected by an HSM-backed RSA key. Shows costs (≈$0.03/10k ops, premium keys ≈$1/key), explains that a key never comes out of the vault, recommends separate vaults per environment, covers secret versioning, HMAC+PBKDF password hardening, and links to MIT‑licensed GitHub code.
AI-written summary · about
chapters (14)
- 0:00Intro
- 3:39Don't Just Focus on Perimeter Security
- 12:18Tamper proof Central key repository Can also store Certs (Private Keys)
- 16:19Once a key goes in the Key Vault, it never comes out again
- 17:43Keys vs Secrets
- 22:57Configuration as Secrets
- 25:14Local Key Wrapping
- 31:19Insurers Pll data encrypted using their own keys
- 33:57Key Versioning
- 35:39Password Protection
- 37:29Salted Hash Passwords
- 46:25Good practice to use different HMAC / Vault Keys for different roles, it Admin, internal employee, customers etc.
- 47:47A digital is a mathematical technique used to validate the authenticity and integrity of a message, software or digital document
- 53:11Data Breaches are Inevitable
related talks
 01h 03mProtecting Encryption Keys with Azure Key Vault
 56mProtecting Encryption Keys with Azure Key Vault
 57mProtecting Encryption Keys with Azure Key Vault
 10mCan you keep it a secret?
 20mAzure Authentication With Vault
 47mManaging your Secrets in a Cloud Environment
 22mSecure your secrets with automation
 43mSecure Development