DevSecOps - what does it mean and where is it taking us?

summary
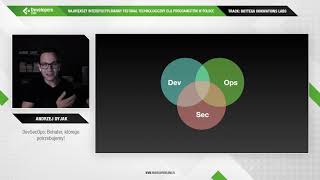
Argues that DevSecOps is DevOps plus security and that the useful pattern is platform self-service tools with guardrails not renaming Ops teams; cites Amazon’s model where teams own code, infra and on‑call duty and research-backed goals like the four metrics from Accelerate (lead time, deploy frequency, MTTR, change-fail rate). Recommends ops/sec build tools that push notifications and enforce standards, requires investment in platform teams, two‑way developer enablement, and yields faster, safer deploys if followed consistently.
AI-written summary · about
chapters (20)
- 0:00Introduction
- 0:31Seb Rose introduction
- 1:37What is devops
- 3:53Books on devops
- 9:34The Dream
- 12:14Scaling the Dream
- 13:44Platform Tools
- 15:02DevSecOps
- 18:49Security Operations Development
- 21:05Security Research
- 24:20Guidelines
- 27:01Developer enablement
- 30:37Whats in the name
- 31:18This is not a pipe
- 32:05Names are important
- 33:10Honest naming
- 33:40Dishonest naming
- 33:52Summary
- 35:09Request for you
- 35:57Wrap up
related talks
 06mDevSecOps is a Misnomer
 23mDevSecOps - By Any Other Name
 49mDevSecOps but Secure! Developing More Securely, Continuously
 39mDevSecOps: What, Why and How
 30mDevSecOps: More Than Just Pipelines
 06mDevSecOps – Security Throughout the DevOps Pipeline
 48mDevOps Is Automation, DevSecOps Is People
 46mDevSecOps: The Hero We Need!