“Everything You Ever Wanted to Know about DLLs”
summary
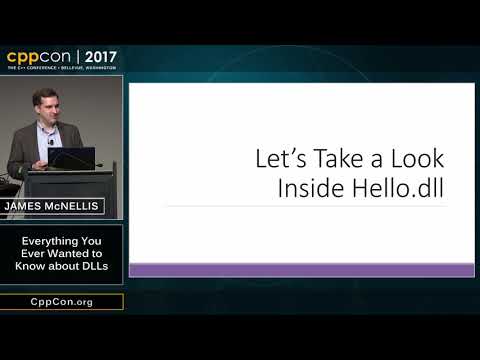
Builds a tiny Hello.dll and PrintGreeting.exe to show exactly what ends up in a Windows PE: DOS stub, COFF header, sections (.text, .rdata), export directory and relocations, inspected with dumpbin and a hex editor; LoadLibrary/GetProcAddress and implicit linking via Hello.lib are demonstrated and the demo runs. Loader behavior (search order, known DLLs, ASLR, relocations), loader steps (map, relocate, bind imports, call DllMain) and diagnostics with Gflags are detailed; advice: use .def for stable exports and avoid exposing C++ ABI.
AI-written summary · about
chapters (8)
- 0:00Introduction to DLLs
- 1:05Building and using a DLL
- 8:33What's inside a DLL file
- 22:46Exporting functions from DLLs
- 35:31Loading a DLL into memory
- 43:43Debugging DLL loading failures
- 50:33C++ and DLLs
- 1:00:00Q&A session
related talks
 59m“C++ in Elvenland”
 01h 04mThe Bits Between the Bits: How We Get to main()
 59mWhat Happens After The Compiler in C++ (How Linking Works)
 31mAmong ELFs and DWARFs
 01h 00mFrom Program to Process - What Happens After the Compiler
 01h 05mHow to Write a Heap Memory Profiler
 59mHello World From Scratch
 01h 02mHow symbols work and why we need them