Temporary Access to the Cloud: A Case Study
summary
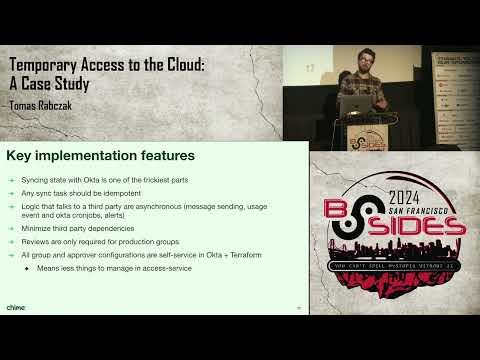
Chime builds a temporary-access service on Okta that uses SCIM-based provisioning, Postgres, Slack reviews, Panther for audit logs, Tines for emergency alerts, strongDM/Snowflake/AWS SSO integrations, and Terraform configs. First commit is Feb 2022 and production cutover Feb 2023; migrations of existing permanent roles show about a 50% drop in unused access after 30 days. Build decision hinges on avoiding an Okta super‑admin key; practical problems include Okta API rate limits that force async processing and retry-safe sync jobs. Two engineers maintain it.
AI-written summary · about
chapters (20)
- 0:00Introduction and speaker intro
- 1:27Problem with permanent access
- 4:44Data on unused access at Chime
- 5:07Design goals for access service
- 6:10Architecture overview
- 10:01Live demo of access service
- 11:28Implementation challenges
- 13:19Terraform configuration
- 15:06Emergency access requests
- 16:09Access request state flow
- 17:10Slack integration for reviews
- 18:16Audit events and compliance
- 18:36Product metrics and North Star
- 21:23Rollout timeline and phases
- 23:50Changing culture of persistent access
- 27:22Build versus buy decision
- 28:06OCTA API rate limits issue
- 30:13What went well in the project
- 31:37Lessons learned and improvements
- 33:25Q&A session begins
related talks
 26mBuilding Blocks of Security: Using passkeys to protect user access
 07mThe Power of Just-In-Time
 31mEnterprise Identity Management on Rails
 28mLessons From a Financial Services Passkey Deployment
 40mSupercharging Cloud Orchestration with Temporal Open Source
 40mManaging Access Entitlements & Their Lifecycle in a Multi-Cloud Environment
 27mLessons Learned Implementing Meaningful Access Controls...
 18mShifting Authentication at Scale