Cybersecurity meets Generative AI: Automating Your Compliance...
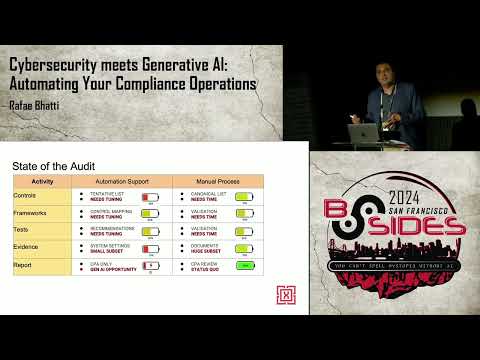
summary
Claim: LLMs can bootstrap compliance ops to cut cost and time by automating mapping, evidence retrieval and draft remediation but require human review. Prototype builds an RAG application and an agentic AI architecture that uses embeddings in a vector DB, zero‑shot prompts and LangChain + gp4 with in‑memory storage; it flags controls as fully/partially/not met and explains why. Current metrics: evidence automation ~20–25%, SOC 2 ~147 controls, HIPAA ~125 total, PCI ~367, end‑to‑end audits still ~2–3 months; prototype works but is early and not production‑ready.
AI-written summary · about
chapters (7)
- 0:00Introduction and context
- 2:04The state of modern audits
- 6:27Red pill vs. blue pill
- 21:35Agentic AI architecture
- 25:16Practical demo and application
- 27:57Implementation challenges
- 29:32Future steps and Q&A
related talks
 15mLightning Talk: Future-Proofing Compliance: Leveraging Knowledge Graphs and AI in Cybe...
 30mCompliance at the Speed of Innovation: Leveraging AI-Driven Automation for Real-Time Regulatory Read
 20mMastering global IoT compliance: How AI simplifies RED and the Cyber Resilience Act
 16mGraph-Powered Compliance: Building Intelligent Regulatory Mapping with AI and Neo4j
 12mLightning Talk: Revolutionize Security GRC: Leverage AI and LLM for Continuous Control...
 30mVibe Coding vs Corporate Governance: AI Innovation Without Breaking Compliance
 33mOperationalizing GenAI Applications with DevOps Practices
 31mRethinking DevOps and DevSecOps with Generative AI: Insights