Contemporary Automatic Program Analysis

summary
Automated and manual analysis combine to find real bugs: a simple script GitHub G.P. runs thousands of code-search queries and surfaces ~1.5M PHP command-injection hits and ~750k Java XSS candidates; static tool rats flags two JPEG heap overflows in a 1997 file with 65,000-byte comment buffers; dynamic instrumentation Valgrind reports the exact invalid writes when fed 70,000 bytes; binary analysis and symbolic engines use Z3 solver and CLE to produce concrete inputs (CLE emits three testcases, Z3 yields value 6) that trigger failures.
AI-written summary · about
chapters (29)
- 0:00Introduction
- 0:19Julian Cohen
- 1:41Program Analysis
- 3:08Vulnerability Research
- 4:35Vulnerability Discovery
- 5:44Presentation Goal
- 6:16Metacharacter Injection
- 7:49Command Injection
- 10:01Type Confusion
- 12:29Implicit Type Conversion Vulnerability
- 13:34Implicit Type Conversion
- 14:35Buffer Overflow
- 15:00Rats
- 18:39FAL Grind
- 19:38BAL Grind
- 21:33QuickSEC
- 22:42After Free Vulnerability
- 23:26Aurora Center
- 25:23Aurora UAF
- 27:06Symbolic Execution
- 29:11Constraint Solving
- 30:54Klee
- 32:16CLE
- 32:49CLE Demo
- 35:08Symbolic Execution Engines
- 37:25Static Analysis Platforms
- 38:43Conclusion
- 39:23Thanks
- 40:05Questions
related talks
 45mFinding Vulnerabilities through Static Analysis and Scripting
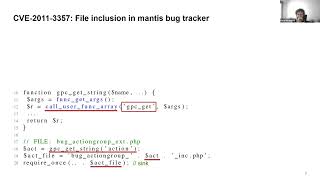 47mWeb Developers, Beware of the Tarpits for SAST in Your Code
 05mWhy Can't Johnny Fix Vulnerabilities: A Usability Evaluation of Static Analysis Tools
 49mOpen-source vulnerability management? Use the source, Luke!
 58mOpen Source Pentesting and Security Analysis Tools: the DevOps way
 44mUsing Static Analysis Tools to Become A Superhero Programmer
 01h 03m“Secure Coding Best Practices: Your First Line Is The Last Line Of Defense (2 of 2)”
 01h 08mAutomated Dynamic Fireware Analysis At Scale: A Case Study on Embedded Web Interfaces