Babar-ians at the Gate: Data Protection at Massive Scale
summary
The talk catalogues concrete failures and fixes in Hadoop deployments: delegation tokens leak in URLs and logs, Kerberos keytabs are written to world‑readable temp files, RM -r by a single Hadoop user can wipe clusters, and redundant namenodes restore availability. Tools discussed include Accumulo for column classification and prototypes like Sentry/Rhino that few teams run in production. Data volumes cited (500 GB/day per turbine blade, engines with up to 20,000 sensors) motivate proxy perimeters, a services layer for ACL checks, and a six‑step PCI‑style control framework.
AI-written summary · about
chapters (20)
- 0:00Intro
- 0:59@daviottenheimer
- 6:46"Predictive Analysis Tool" Rear View Mirror
- 7:30Racecar Competitive Advantages • 1911 Rear-view mirror • 1911 Aerodynamics
- 8:10Seatbelt Timeline to Adoption
- 8:20Big Data Seatbelts?
- 9:14Threat Modeling
- 19:36Emperor's New Controls
- 19:55Control Opportunities
- 20:47Big Data Control Areas
- 21:18A Simple "How To" Framework 1. Net and System Security 4. Access Control
- 22:31Progress to consider
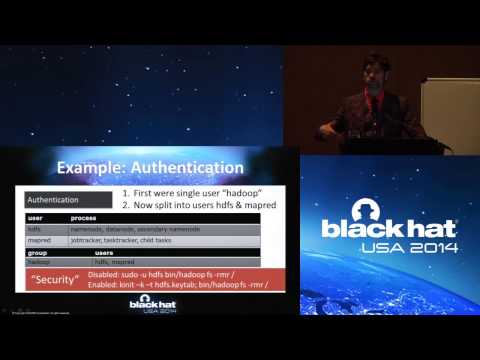
- 24:30Example: Authentication
- 29:07Realities of Securing Big Data
- 30:07Phase Two - Availability
- 31:01Phase Three - Classification
- 31:18Phase Four - Authority
- 32:03Phase Five - Least Authority
- 37:37The Snow Den Lesson CHOLERA VORONI
- 38:39Systematic Treatment = Resilience
related talks
 01h 09mHadoop Security: Seven Ways to Kill an Elephant
 31mRings of Security for Big Data in Cloud
 10mAdding Security to Hadoop
 37mOf Data Dropboxes and Data Gloveboxes
 29mIdentity Management in the Era of Big Data: The intersection of APIs, Hadoop & IdM
 57mBig Data: Threat or Opportunity?
 08mHadoop and Big Data Hype
 34mAvoiding Big Data Antipatterns