Cloud Hacking Scenarios
summary
Finds show a public Kubernetes API with RBAC disabled exposes base64 secrets that reveal AWS keys with only S3/Lambda access, then Jenkins credentials in a configmap allow kubectl port-forward to Jenkins, shell access to the pod and discovery of a Jenkins-assigned IAM role with full AWS admin, yielding account takeover. Separate cases use a hard-coded encryption key in a public GitHub repo to decrypt Office365 creds, then a SharePoint PDF with Jira admin creds that lead to AWS admin keys.
AI-written summary · about
chapters (9)
- 0:00Start
- 5:41Public resources
- 7:11Disabled security features
- 8:28Principle of Least Privilege
- 13:16Prod data on a non-prod environment
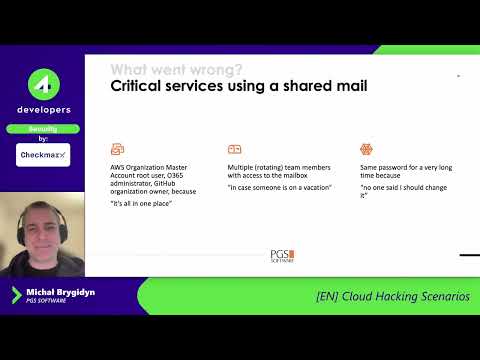
- 15:10Critical services using a shared mail
- 22:16Hardcoded sensitive data
- 24:43Bad tools selection
- 28:13Lack of security awareness
related talks
 36mCloud Hacking Scenarios
 33mCloud Hacking Scenarios
 33mLive Hacking Cloud Architectures - Thorsten Jakoby and Mirna Alaisami
 45mLive Hacking Cloud Architectures
 45mLive Hacking Cloud Architectures
 28m"PIVOT!" — Bouncing between your app, your cluster and your cloud
 19mHacking Kubernetes
 33mHack Back; Let’s Learn Security With CTFs!