Cloud Hacking Scenarios

summary
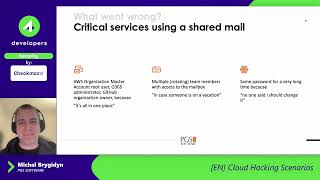
Finds concrete exploit chains: admin AWS keys in JS comments lead to immediate cloud access; public k8s API with RBAC disabled exposes base64 secrets, yields Jenkins admin via port‑forwarding, and a pod with an IAM role escalates to full admin; a Symfony profiler leak gives an inbox used to reset a root AWS password that controls 40–50 organization accounts; a GitHub repo encrypts secrets but hardcodes the decryption key, exposing Office365 and Jira admin creds. Actionable failures and fixes (RBAC, secret managers, MFA, rotation).
AI-written summary · about
chapters (6)
- 0:00Start
- 7:18Public resources
- 8:27Disabled security features
- 10:28Principle of Least Privilege
- 27:29Bad tools selection
- 30:09Lack of security awareness
related talks
 31mCloud Hacking Scenarios
 33mCloud Hacking Scenarios
 46mAttacking AWS: The Full Cyber Kill Chain
 47mBreaking the Cloud to Rebuild It: A Tale of 3 ☁️ Breaches!
 45mLive Hacking Cloud Architectures
 40mBlind Spots: Two Cloud Threats You Didn’t Even Know You Had
 38mAdventures in Cloud Security: What DevOps Can Learn from a Security Engineer
 43mHacking the Cloud: Play-by-Play Attack on GitHub, Okta, and Salesforce