Because Security Matters: Securing Your Open Sourc...

summary
Explains concrete defenses: SUSE locks builds into per-job VMs with the open build service, publishes full provenance at sources.suse.com, signs packages, and pursues SALSA and EAL4+ common‑criteria coverage. For operations, SUSE uses SUSE Manager to enforce patch schedules, scan CVEs and scale from 10 to a million clients; Office Depot case yields ~40% lower IT management cost. Cites rising supply‑chain incidents, 56% of breaches from 4+ year old vulns, and multi‑million dollar outage and breach costs.
AI-written summary · about
chapters (8)
- 0:00Start
- 1:08Supply Chain Attacks
- 2:38The Four Winds Hack
- 3:53The Secure Supply Chain
- 5:26Human Errors
- 8:51Build Threats
- 9:34Dependency Threats
- 35:58Managing Your Infrastructure
related talks
 45mSponsored Session: Because Security Matters: Securing Your Open Source Supply Chain
 39mOpen Source Software Supply Chain Security — Why does it matter?
 09mSecuring the Software Supply Chain with Open Source
 29mSecuring the Unseen: Defending Against Open Source Software Supply Chain Attacks
 40mSecurity: Why It _has_to Be Open Source
 29mSupply Chain Security: Threats, Defenses And What You Can Do
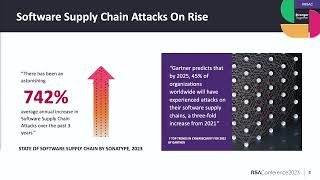 49mScaling Software Supply Chain Source Security in Large Enterprises
 54mSupply Chain Security for OpenSource Projects