Practical TLS Advice for Large Infrastructure

summary
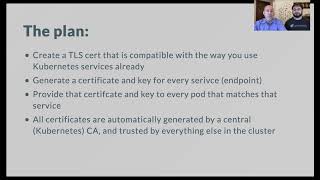
Argues that TLS must be applied everywhere in large deployments and that ACME or service meshes alone do not solve certificate authority architecture. Recommends 90 days or shorter lifetimes, Certificate Transparency, and automated rotation; shows Kubernetes issuing pod certificates to enforce mutual TLS between pods (prevents MITM) and lists tools: cert-manager and Vault, CFSSL, Istio, and cloud HSMs. Describes storing key+cert+CA in app secrets and monitoring with Prometheus blackbox to alert before expiry.
AI-written summary · about
chapters (12)
- 0:00Intro
- 1:50The Public Trust Domain
- 8:30Building Trust on the Web
- 10:32Getting Certificates into Applications
- 12:04Application Architecture
- 14:27Certificate Transparency
- 16:59Local Trust Domains
- 19:23Trust Model
- 21:17Certificate Management
- 25:31Summary
- 28:13Monitor your certificates
- 29:26Remote trust domains
related talks
 24mOur Journey of Implementing TLS at Scale for Services on Kubernetes
 31mHow We Solved TLS at Scale: Self-Service, Multi-Tenant Cert-manager
 15mCertificates in Kubernetes
 46mContinuous Kubernetes Security
 31mPKI the Wrong Way: Simple TLS Mistakes and Surprising Consequences
 20mTrust Agility in an Era of Transient Ties: Rethinking TLS...
 36mYou Like It Or Not; You Need It! - PKI And Certificate Management
 32mAchieving Mutual TLS: Secure Pod-to-Pod Communication Without the Hassle